
On CentOS 6.x, the firewall is the iptables service, plus ip6tables for IPv6. Turning it off is a common step when you’re troubleshooting a service that can’t be reached. You might also want it off on a lab box behind another firewall. Here is how to stop it, keep it off after a reboot, and check the result.
1. Become root
su -
2. Stop the firewall now
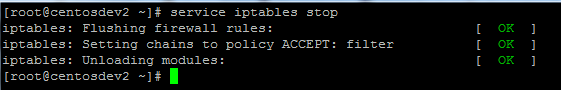
service iptables stop
service ip6tables stop
This flushes the rules and sets the default policies to ACCEPT, so traffic is no longer filtered.
3. Keep it from starting at boot
Stopping the service only lasts until the next reboot. Use chkconfig to disable it in every runlevel:
chkconfig iptables off
chkconfig ip6tables off
4. Verify
service iptables status
chkconfig --list iptables
iptables -L -n
service iptables status should report that the firewall is not running. chkconfig --list should show off for runlevels 0 through 6, and iptables -L -n should show empty chains with policy ACCEPT.
A better option: open just the port you need
If you only want one service reachable, you don’t have to turn the whole firewall off. Add a rule and save it to /etc/sysconfig/iptables:
iptables -I INPUT -p tcp --dport 80 -j ACCEPT
service iptables save
Don’t forget SELinux and TCP wrappers
If a service still can’t be reached with the firewall off, the firewall wasn’t the problem. Check that the daemon listens on the right address with netstat -tlnp, see whether SELinux is blocking it with getenforce and /var/log/audit/audit.log, and look at /etc/hosts.allow and /etc/hosts.deny.
Turning it back on
chkconfig iptables on
service iptables start
On CentOS 7, RHEL 8/9 and AlmaLinux
Newer releases use firewalld instead of the iptables service. The equivalents are:
systemctl disable --now firewalld
systemctl status firewalld
To open a single service instead:
firewall-cmd --permanent --add-service=http
firewall-cmd --reload
To get a Hosted CentOS Linux Server visit www.zwiegnet.com/go to get started today!
Related guides: Disable SELinux CentOS 7 | Configure Fail2Ban on CentOS