
Configure Fail2Ban on CentOS
Configure Fail2Ban on CentOS
Fail2Ban is a nice little piece of software that scans logs, and determines when an IP address needs to be blacklisted, and detects other types of malicious activities.
** NOTE THIS BLOG ASSUMES YOU ALREADY HAVE IPTABLES CONFIGURED/Working Knowledge of IPTABLES **
Let’s get started, login and su to root

From here we need to install the EPEL Repository
Install the Epel Repo
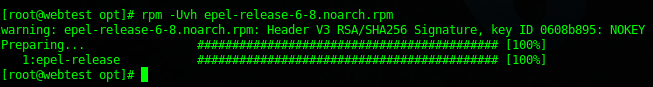
now we can proceed further….
Install the Fail2Ban Package using the following command:

once installed we need to copy the default config file so we can configure it

now edit the new config

now customize the appropriate moudle you are trying to lock down, SSH is a really good example of a service that if you are goofy enough to run it externally, you at least want to have a “lockout”
Take a look at the first Section:
[DEFAULT]

# "ignoreip" can be an IP address, a CIDR mask or a DNS host. Fail2ban will not
# ban a host which matches an address in this list. Several addresses can be
# defined using space separator.
ignoreip = 127.0.0.1 (should be configured as Local IP Address of Server)

# "bantime" is the number of seconds that a host is banned.
bantime  = 3600

# A host is banned if it has generated "maxretry" during the last "findtime"
# seconds.
findtime  = 600

# "maxretry" is the number of failures before a host get banned.
maxretry = 3
Moving on, find the section titled [ssh-iptables]
[ssh-iptables]
enabled = true
filter = sshd
action = iptables[name=SSH, port=ssh, protocol=tcp]
sendmail-whois[name=SSH, dest=you@example.com, sender=fail2ban@example.com, sendername=”Fail2Ban”]
logpath = /var/log/secure
maxretry = 5
customize the above entry for hte proper emails, Sender Name, Etc
Once Configured, set the service to run on startup, and manually start the service
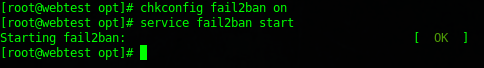
if you do an iptables -L, you should see the following:
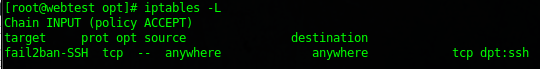
That’s it! You have successfully configured Fail2Ban!
Related guides: Configure SSH Key Authentication Only | Disable Iptables CentOS 6.4
1 Comment