Copy LDAP to Another Server

Copy LDAP to Another Server

Copy LDAP to Another Server

In this scenario, we are going to copy our primary ldap database to our secondary LDAP server and re-apply/update with a more current version. Here’s the basic process:

login on your primary LDAP server, and su to root
Root shell prompt on the primary OpenLDAP server ldapdemo after su to root

from here change to the /tmp directory where we manipulate the LDAP database

Running ldapsearch -x > ldapdb in /tmp on the primary LDAP server to dump the directory

from here do a dump of the ldap database

Running ldapsearch -x > ldapdb on the primary OpenLDAP server to save every entry to a file

perfect, now from here we are going to login to our 2nd ldap server
Root shell prompt on the secondary OpenLDAP server ldapdemo2

cd /tmp

Running cd /tmp on the secondary LDAP server ldapdemo2

now we sftp to our primary LDAP server

Running sftp ldapserver1 from the secondary server to connect to the primary LDAP server

you should be greeted with the following:

sftp> prompt after connecting to the primary LDAP server

change to the /tmp directory

Running cd /tmp inside sftp on the primary LDAP server

this next command downloads the LDAP database from the original LDAP server
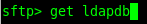
Running get ldapdb in sftp to download the LDAP dump from the primary server

done, here’s what the download should have looked like
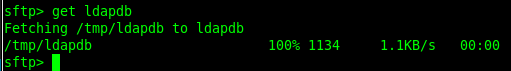
sftp output fetching /tmp/ldapdb to ldapdb at 100 percent

now exit from sftp

Running exit to close the sftp session

stop the LDAP service

Running service slapd stop on the secondary OpenLDAP server

from here remove the present info/database

Running rm -rf /var/lib/ldap/* on the secondary server to remove the old LDAP database

start the LDAP service with an empty database
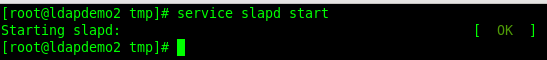
Running service slapd start on the secondary server with an empty LDAP database

from here add the file to re-create the database

Running ldapadd -x -D cn=admin,dc=mydomain,dc=local -W -f /tmp/ldapdb to load the copied entries

type in your LDAP admin password

Enter LDAP Password prompt from ldapadd on the secondary server

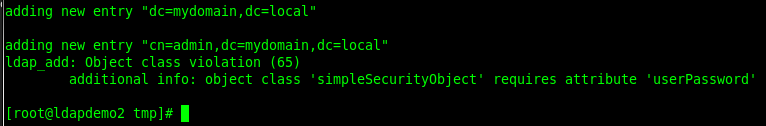
you should see something like this:

ldapadd output adding entries, with an object class violation for the cn=admin entry's missing userPassword

obviously you will get the error that it cannot update your admin password, because that would break LDAP.

let’s re-dump the database to make sure all is well

Running ldapsearch -x > ldapdb on the secondary server to dump the rebuilt directory

now vi the ldapdb

Running vi ldapdb on the secondary server to check the copied entries

cool, we can see our most recent entry John Smith is in there.
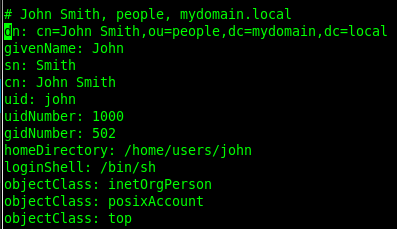
Copied LDAP entry for John Smith, ou=people, dc=mydomain, dc=local on the secondary server

done! we made a copy of LDAP, and moved it to another server.

Hosted Linux Servers at www.zwiegnet.com/go

Related guides: LDAP Replication CentOS 6 | Configure LDAP Server on CentOS 6

Leave a Reply

Your email address will not be published. Required fields are marked *