Umask CentOS 6 Permissions
Umask CentOS 6 Permissions
Let’s face it, the default perimssions for CentOS 6 are a pain. Basically only owner can do anything, it completely ignores basic colaboration of departments. Why? My guess is it’s some sort of security standard, need-to-know. That’s great, except for that standard users don’t have access to chmod, nor would they learn that, or changing permissions manually on a file, so that is all less than optimal.
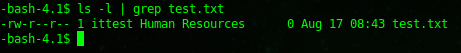
Let’s talk about configuring a UMASK, you can configure this either on the server level, or the account level. If you are in a production environment, changing this on a server level isn’t really the best way to do it, and you have to remember to add it to each new server at the time of the build. OR…. you can add it to each users .profile. It’s a horse a piece scenario.
Ideally, for this environment LDAP users would want to have 770/660 permissions that way only them, and group members have access, if you want seperate access, then you can set it to readable by other groups, etc.
Login to you NFS server, and browse to your /home (or if you foolishly have home directories somewhere else, browse there).
change to the user you would like to test to
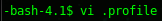
vi .profile (this file may not exist)
append the following 3 lines to the .profile
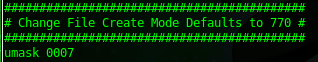
basically setting the umast to 0007 sets 770 permissions, and 660 permissions for files/folders.
To get a better understanding on umask, go here
you can also issue temporary umask permissions to test using the “umask” command ex: umask 022
This setting takes effect after logging out, and back in again, including for GNOME/KDE.
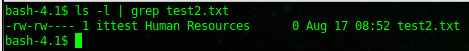
create a test file called test2.txt
view the permissions
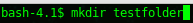
ok, now let’ check a folder
view permissiosn
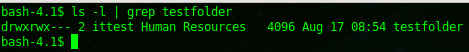
perfect!
as you can see we have configured 770/660 permissions for files/folders via Umask.
Hosted Linux Servers at www.zwiegnet.com/go
Related guides: Understanding Linux File Permissions | Setfacl using LDAP Groups